 FHN
Cybercriminals are finding new ways to keep malware connected to their infrastructure, and this time they are turning to the Ethereum blockchain.
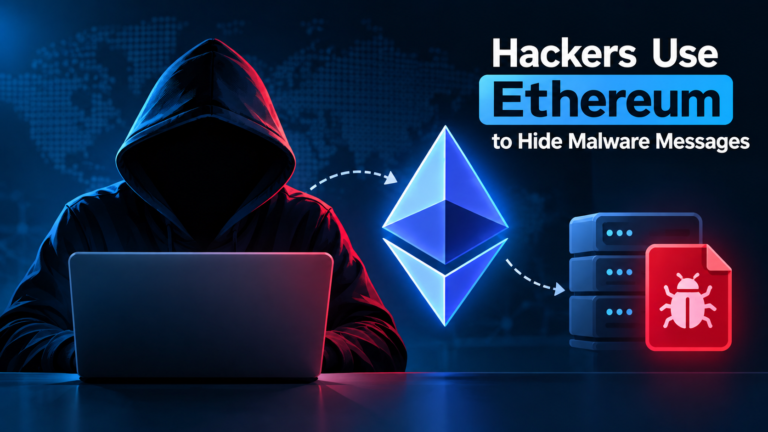
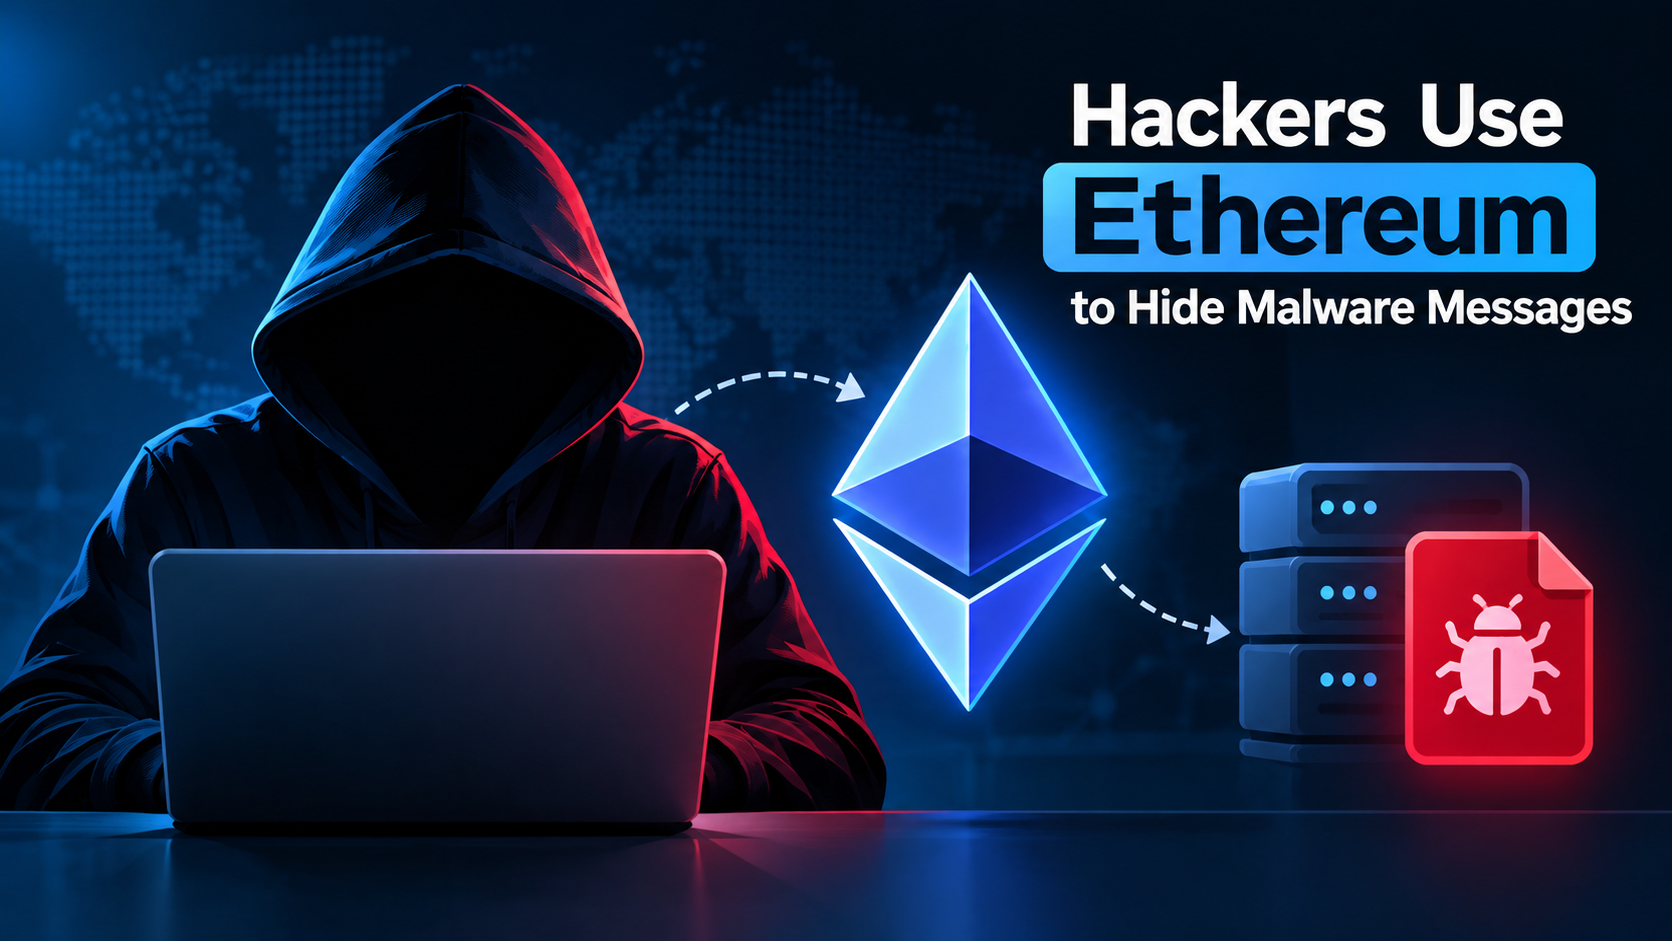
Researchers have uncovered a campaign linked to North Korea that uses Ethereum transactions to secretly tell infected computers where to find their command server. The blockchain is not being used to store the malware. Instead, it works more like a public notice board that the malware can check for new instructions.
The campaign appears to focus heavily on software developers. Victims may encounter the malware through fake recruitment offers, infected software projects, or malicious packages. Once the code is executed, additional malware can be installed on Windows, macOS, and Linux systems.
Researchers from Ransom-ISAC identified the technique in recent samples of the XCTDH malware family.
Ethereum Becomes a Communication Channel
The attackers have developed a clever way to hide server information inside an Ethereum transaction.
Rather than placing a complete command or malware file on the blockchain, the malware looks for a transaction from a specific wallet controlled by the attackers. Information encoded in the transaction’s destination address can reveal the IP address and port of the server the malware should contact.
The infected machine regularly checks recent Ethereum blocks. When it finds the expected transaction, it extracts the hidden information and attempts to connect to the newly identified server.
This gives the attackers an easy way to change their infrastructure without sending a new version of the malware to every infected computer.
Researchers observed the campaign changing its encoded server information several times. During a 90-day observation period, they identified 2,655 Ethereum transactions associated with the activity.
The technique is particularly interesting because the blockchain itself remains legitimate. There is no need to hide a large malicious file inside an Ethereum transaction.
The Malware Uses Several Backup Routes
Ethereum is not the campaign’s only communication method.
The malware also uses other blockchain networks as part of its infrastructure. Researchers found references to TRON and Aptos, while additional encrypted JavaScript was associated with transactions on the BNB Smart Chain.
Using several communication paths gives the attackers more flexibility. If one server disappears or one route is blocked, the malware may still have another way to obtain information.
The initial infection can begin with a developer-focused social engineering attack. A fake job opportunity or seemingly legitimate coding project may convince a victim to execute malicious code.
After that, the malware can establish remote access and collect information from the compromised system.
Researchers observed capabilities including:
- Remote command execution
- Keystroke monitoring
- Clipboard collection
- Browser data theft
- Password-manager information theft
- Cloud credential collection
- Cryptocurrency wallet targeting
A separate stealer component was also found targeting numerous cryptocurrency wallets.
Why This Technique Is Difficult to Disrupt
The biggest challenge for defenders is that blockchain data is public and persistent.
An attacker can publish a new server address through a blockchain transaction, and infected systems can discover it without receiving a traditional configuration update.
That means blocking a known IP address may only solve part of the problem. If the malware can obtain another address from the blockchain, it may simply attempt to reconnect using the new infrastructure.
Ransom-ISAC recommends that security teams look for unusual blockchain-related activity, especially when it is followed by unexpected outbound connections.
Organizations should also pay close attention to developer environments, particularly:
- Suspicious Node.js activity
- Unexpected code execution
- Malicious or unusual packages
- Unknown JavaScript loaded by development projects
- Unusual connections from developer machines
- Blockchain queries followed by network connections
This campaign shows how attackers are adapting familiar technologies for malicious purposes. A blockchain transaction may look like an ordinary piece of cryptocurrency activity, while malware can interpret it as an instruction to reconnect to its operators.
For defenders, this means blockchain traffic may need to be considered alongside traditional domains, IP addresses, and command-and-control indicators when investigating modern malware campaigns.
About the Author