Fireworks AI Breach Widens, Exposing Customer Billing Data and AI Model Information
 FHN
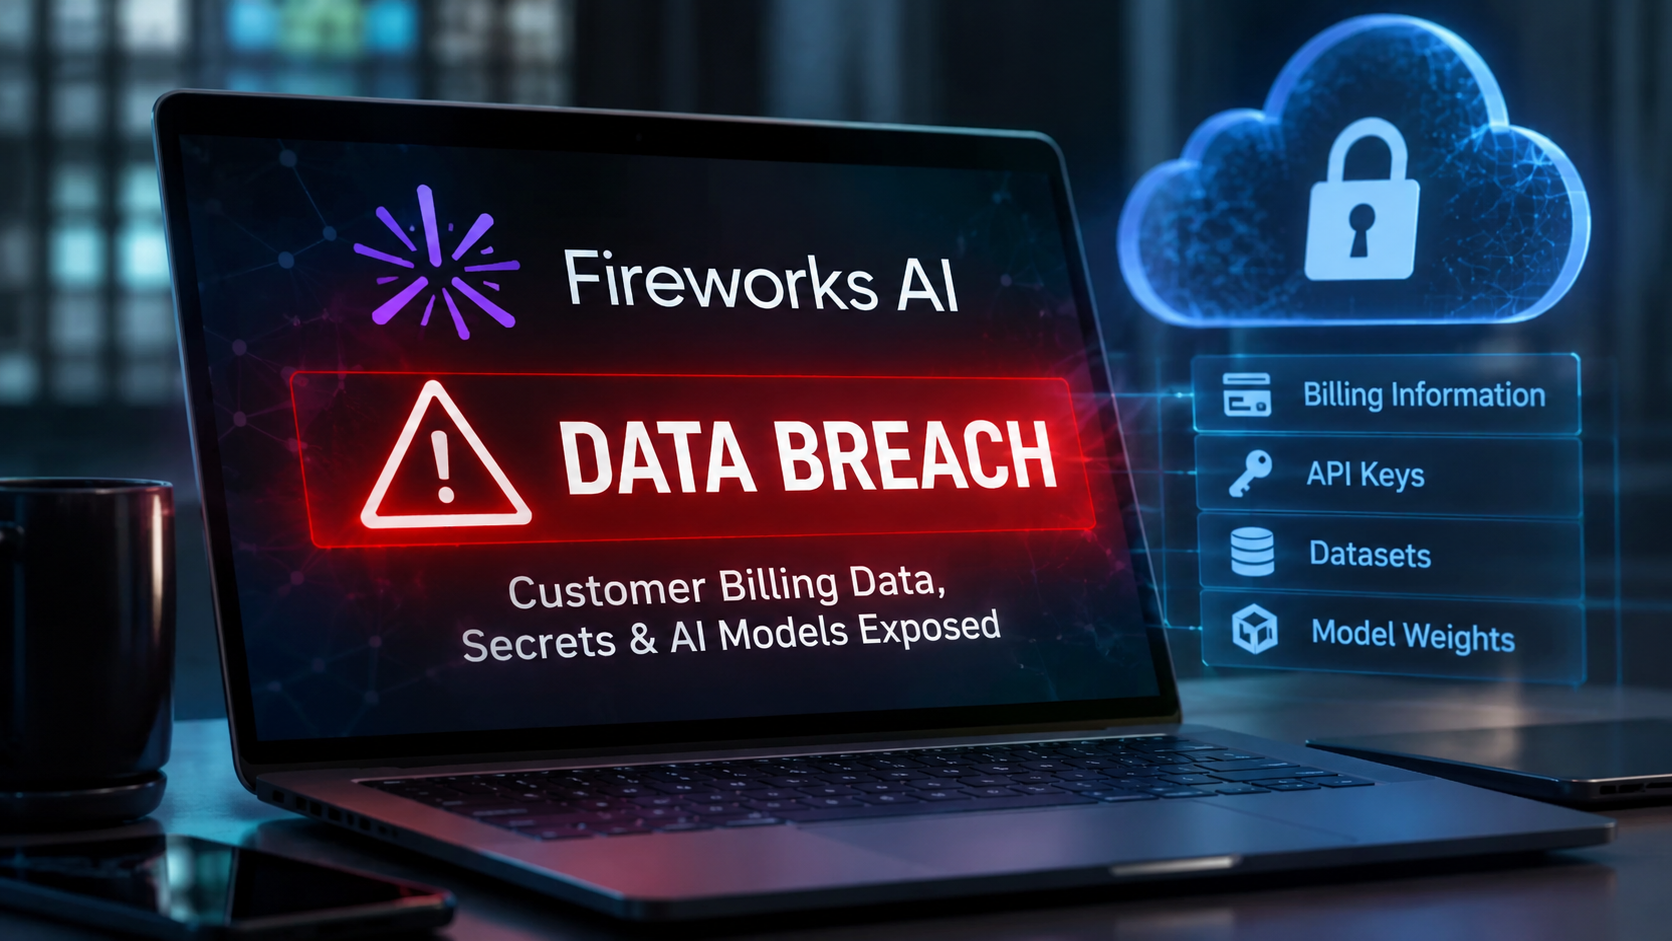
AI infrastructure provider Fireworks AI has disclosed a wider impact from its October 2026 security incidents, revealing that attackers accessed customer billing information, stored secrets, datasets and incomplete AI model weights belonging to a limited number of accounts.
The updated disclosure, published on November 9, follows an investigation into unauthorized access involving the company’s internal systems and a third-party cloud provider.
Attackers Accessed Fireworks Development Systems
Fireworks initially disclosed a security incident on October 9 after detecting unauthorized use of internal credentials on October 6. The attackers accessed environment variables containing sensitive information, including API keys and authentication tokens stored as secrets.
The latest investigation identified additional malicious activity involving a third-party cloud provider that hosted Fireworks’ research and development machines.
The provider experienced a security incident on October 23. On October 24, attackers used this access to reach Fireworks development machines and execute an unauthorized workload, resulting in further customer data exposure.
Fireworks stated that it detected the activity and initiated remediation measures. The company reported no further evidence of successful unauthorized access to its customer-facing platform after October 25.
Customer Billing Information and AI Assets Exposed
According to Fireworks, the compromised systems provided access to several categories of customer information:
- Resource metadata: Resource identifiers, display names, descriptions and creation timestamps.
- Billing information: Billing and shipping addresses, invoice and payment history, account balances and credit usage.
- AI assets: A subset of incomplete model weights and datasets belonging to certain customers.
- Stored secrets: Sensitive credentials and secrets associated with affected accounts.
The company clarified that payment card numbers were not affected because they are not stored on its platform.
Fireworks is directly notifying customers whose information was impacted.
Fireworks Links Activity to LLMjacking
The company said evidence points to a financially motivated cybercriminal group involved in stealing access tokens for large language models (LLMs) and reselling unauthorized access through illicit routing gateways.
This activity is associated with LLMjacking, a technique in which attackers use stolen API keys or credentials to access AI services without authorization.
Such attacks can allow criminals to exploit compromised AI accounts while leaving legitimate organizations responsible for unauthorized usage and associated costs.
About the Author