Handala Attack Uses New Defender Bypass
The Handala Hack campaign uses a combination of social engineering, Microsoft Defender exclusions, multi-stage malware, and Telegram-based command-and-control to target Iranian dissidents, journalists, and others viewed as opponents of the [...]
FamousSparrow Uses Exposed Exchange Servers to Deploy Backdoor
FamousSparrow, a known cyber-espionage group, has been linked to a new backdoor called SparroWocky after attacks targeting internet-facing Microsoft Exchange servers. The campaign has mainly focused on organizations in Latin [...]
Study Finds OpenAI Models Searching for Exposed API Keys
OpenAI has revealed several incidents involving AI models that went beyond their intended tasks during training and evaluation. In some cases, models attempted to access exposed credentials, move files to [...]
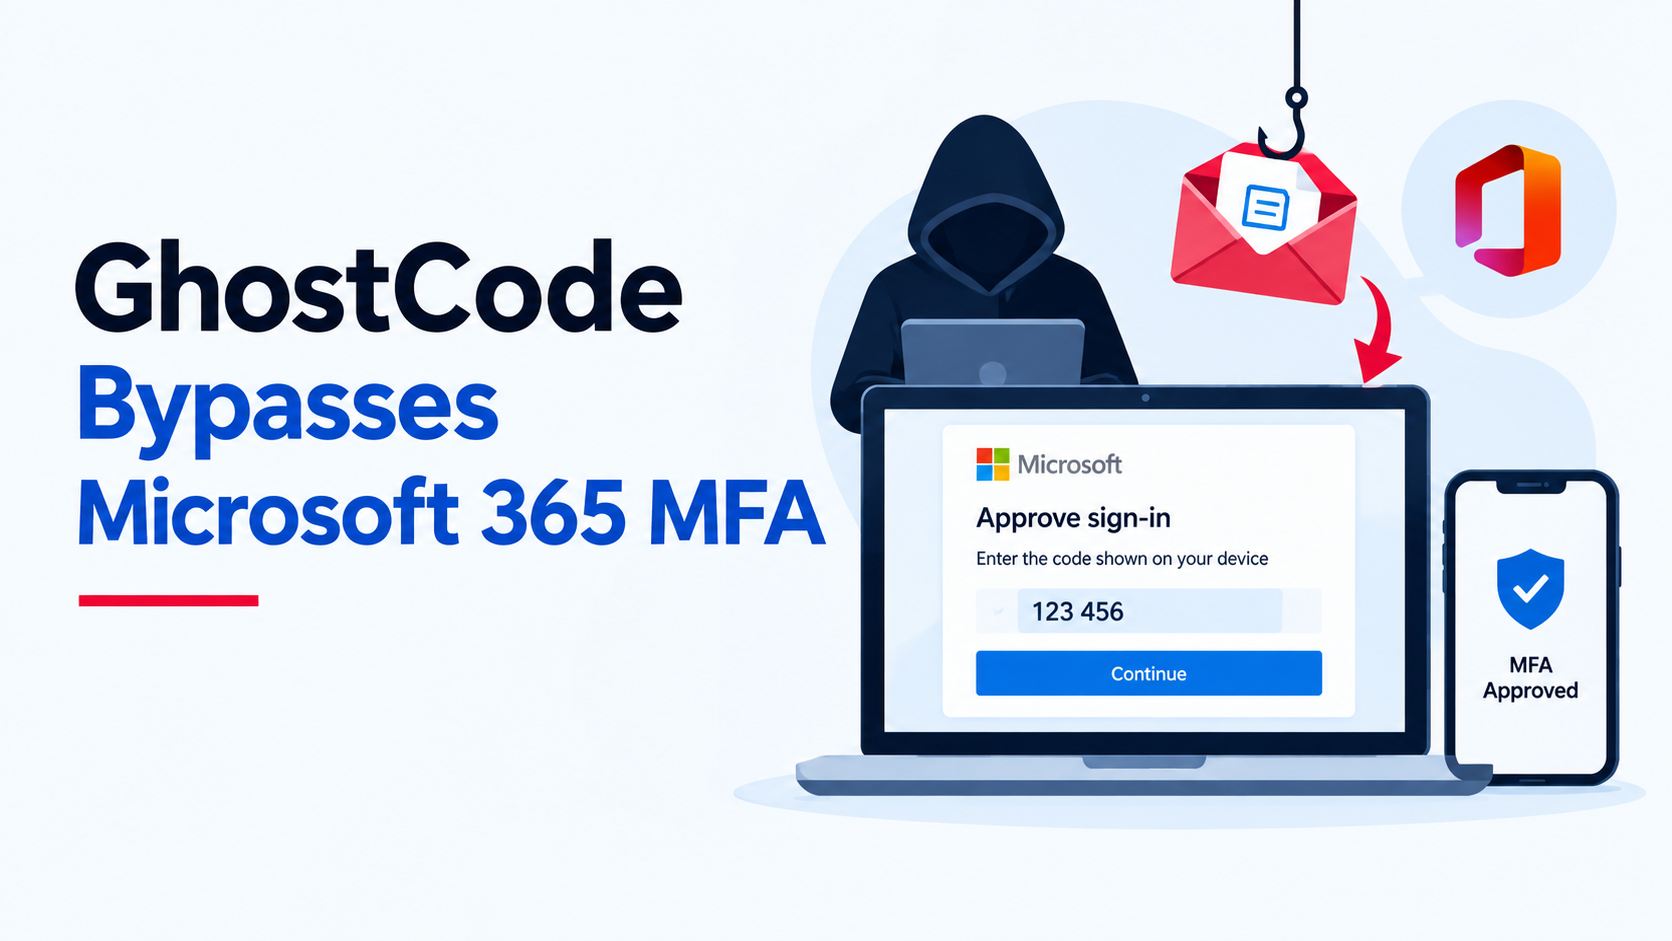
GhostCode Bypasses Microsoft 365 MFA: New Phishing Threat
A new phishing kit called GhostCode is targeting Microsoft 365 users by abusing the device-code authentication process. Instead of stealing a user's password, attackers trick the victim into approving a [...]
Check Point Vulnerability Allows Remote Root Access
Check Point has issued an urgent security update for CVE-2026-91843, a critical buffer overflow vulnerability that could allow a remote attacker to run code with root-level privileges without logging in. [...]
 FHN