 FHN
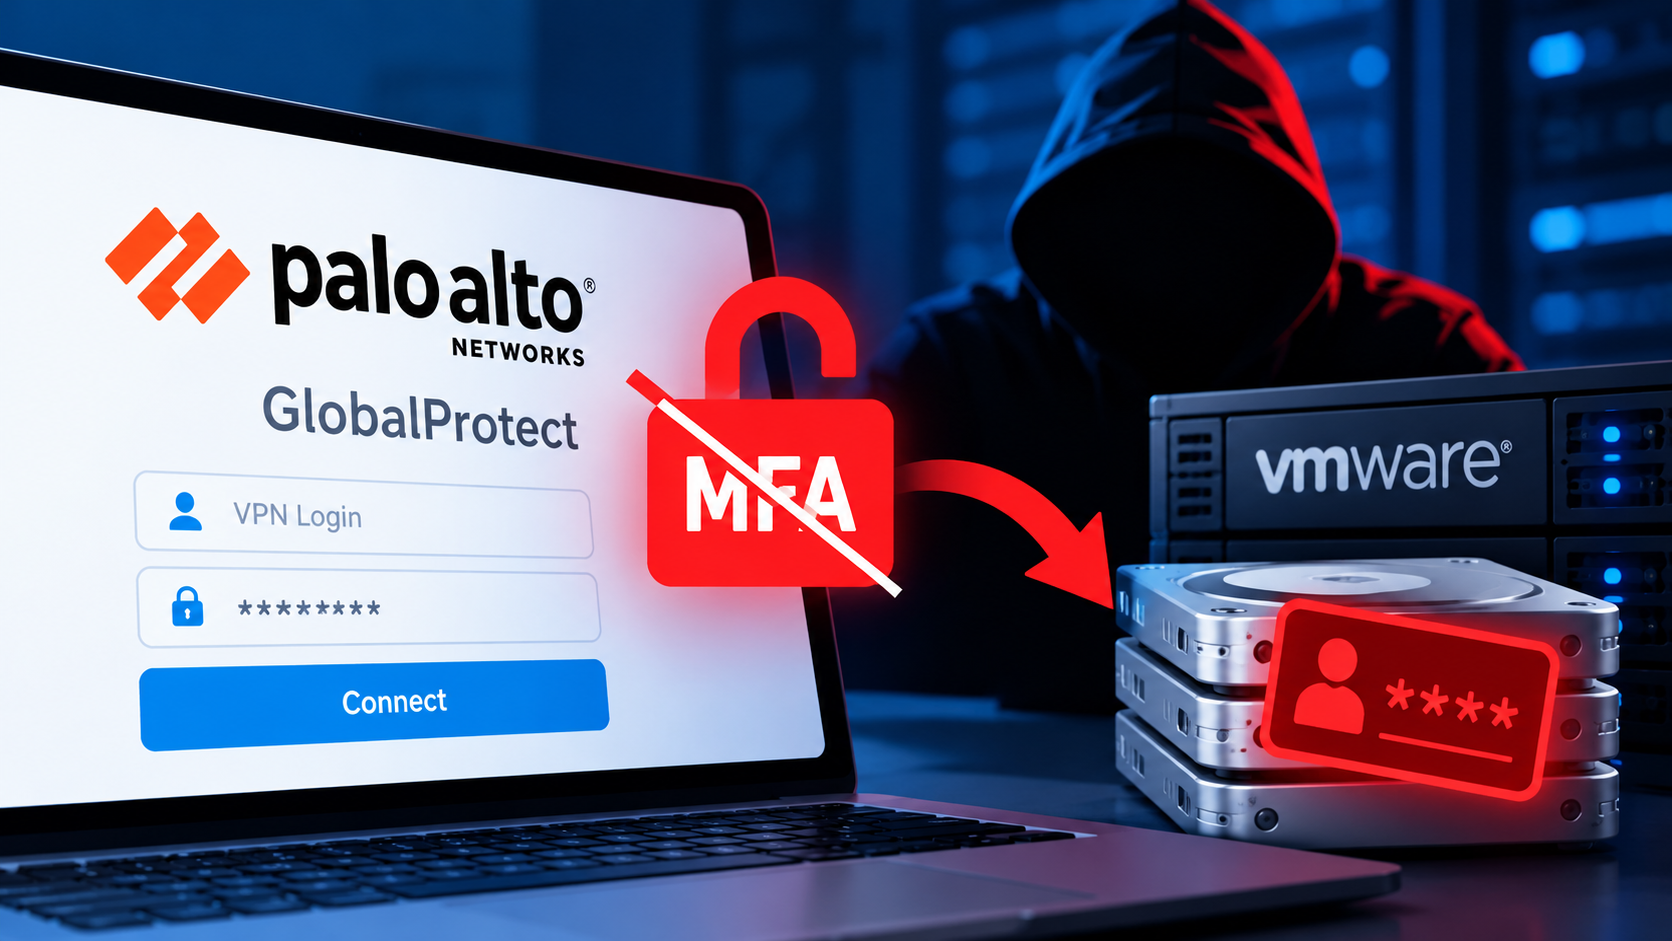
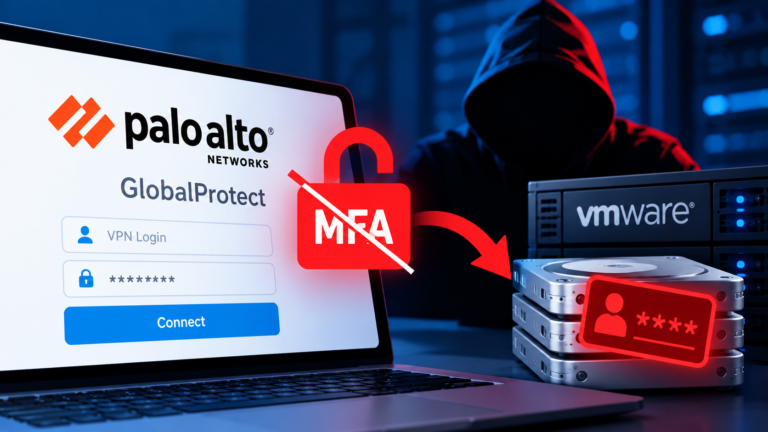
Cybersecurity researchers have reported ransomware operators exploiting a vulnerability in Palo Alto Networks GlobalProtect VPN to gain unauthorized access to corporate networks.
Tracked as CVE-2026-0257, the flaw affects certain PAN-OS and Prisma Access configurations. Attackers may bypass normal login protections, including multi-factor authentication (MFA), and establish unauthorized VPN connections.
In an October 19, 2026, update, Palo Alto Networks Unit 42 linked exploitation attempts to ransomware groups known as Qilin and Inc. Public reporting has also associated attacks with Settra ransomware. <Cite refs={[“turn898104view0″,”turn898104view1”]}/>
How the VPN Attack Works
The vulnerability involves the way GlobalProtect handles authentication override cookies. These cookies allow users to reconnect without completing the full authentication process each time.
Certain vulnerable configurations may accept forged cookies, allowing attackers to bypass normal authentication checks. Exposure depends on the device configuration, including the use of authentication override cookies and a specific certificate setup. <Cite refs={[“turn898104view1”]}/>
Once attackers gain access, they may attempt to move deeper into the network and prepare for further attacks.
Researchers reported the following activities:
- Using remote monitoring tools to explore internal networks.
- Moving between systems through Remote Desktop Protocol (RDP) and Server Message Block (SMB).
- Preparing tools to collect credentials and steal data.
- Targeting virtualization and backup infrastructure.
In one investigated case, attackers reached VMware vCenter and accessed a domain controller’s virtual disk to extract credentials offline. This technique can bypass security tools operating inside the affected virtual machine.
Researchers also observed activity involving Veeam backup infrastructure, highlighting the risk to systems organizations rely on to recover from ransomware attacks. <Cite refs={[“turn898104view0”]}/>
How Organizations Can Protect Their Networks
Palo Alto Networks has rated the vulnerability High severity, with a CVSS score of 7.8, and recommends urgent action for affected deployments. <Cite refs={[“turn898104view1”]}/>
Security teams should take these steps:
- Install security updates: Upgrade affected PAN-OS and Prisma Access deployments to the fixed versions listed in the official security advisory.
- Review authentication settings: Disable authentication override if it is not required, or use a dedicated certificate exclusively for authentication override cookies.
- Check VPN logs: Investigate successful
gateway-connectedevents associated with suspicious IP addresses, device names, or host identifiers. - Inspect internal activity: Look for unusual RDP and SMB connections, unexpected access to vCenter, and suspicious credential access.
- Protect backup systems: Review Veeam and other backup infrastructure for unauthorized access or unusual activity.
Unit 42 has published indicators to help defenders investigate suspicious VPN connections. Its report notes that many observed probes did not establish successful VPN sessions, so security teams should focus on confirmed connections and investigate them promptly. <Cite refs={[“turn898104view0”]}/>
Final takeaway: A VPN is a critical entry point into an organization’s network. Regular patching, secure authentication settings, and monitoring for suspicious activity are essential to preventing unauthorized access and limiting the impact of ransomware attacks.
About the Author